
Secure Edge‑Computing Nodes with Raspberry Pi 5 and Zero‑Trust WireGuard
Learn how to build a hardened Raspberry Pi 5 edge node for industrial IoT, harden the OS, and set up WireGuard zero‑trust tunnels to meet today’s data‑localization and security demands.
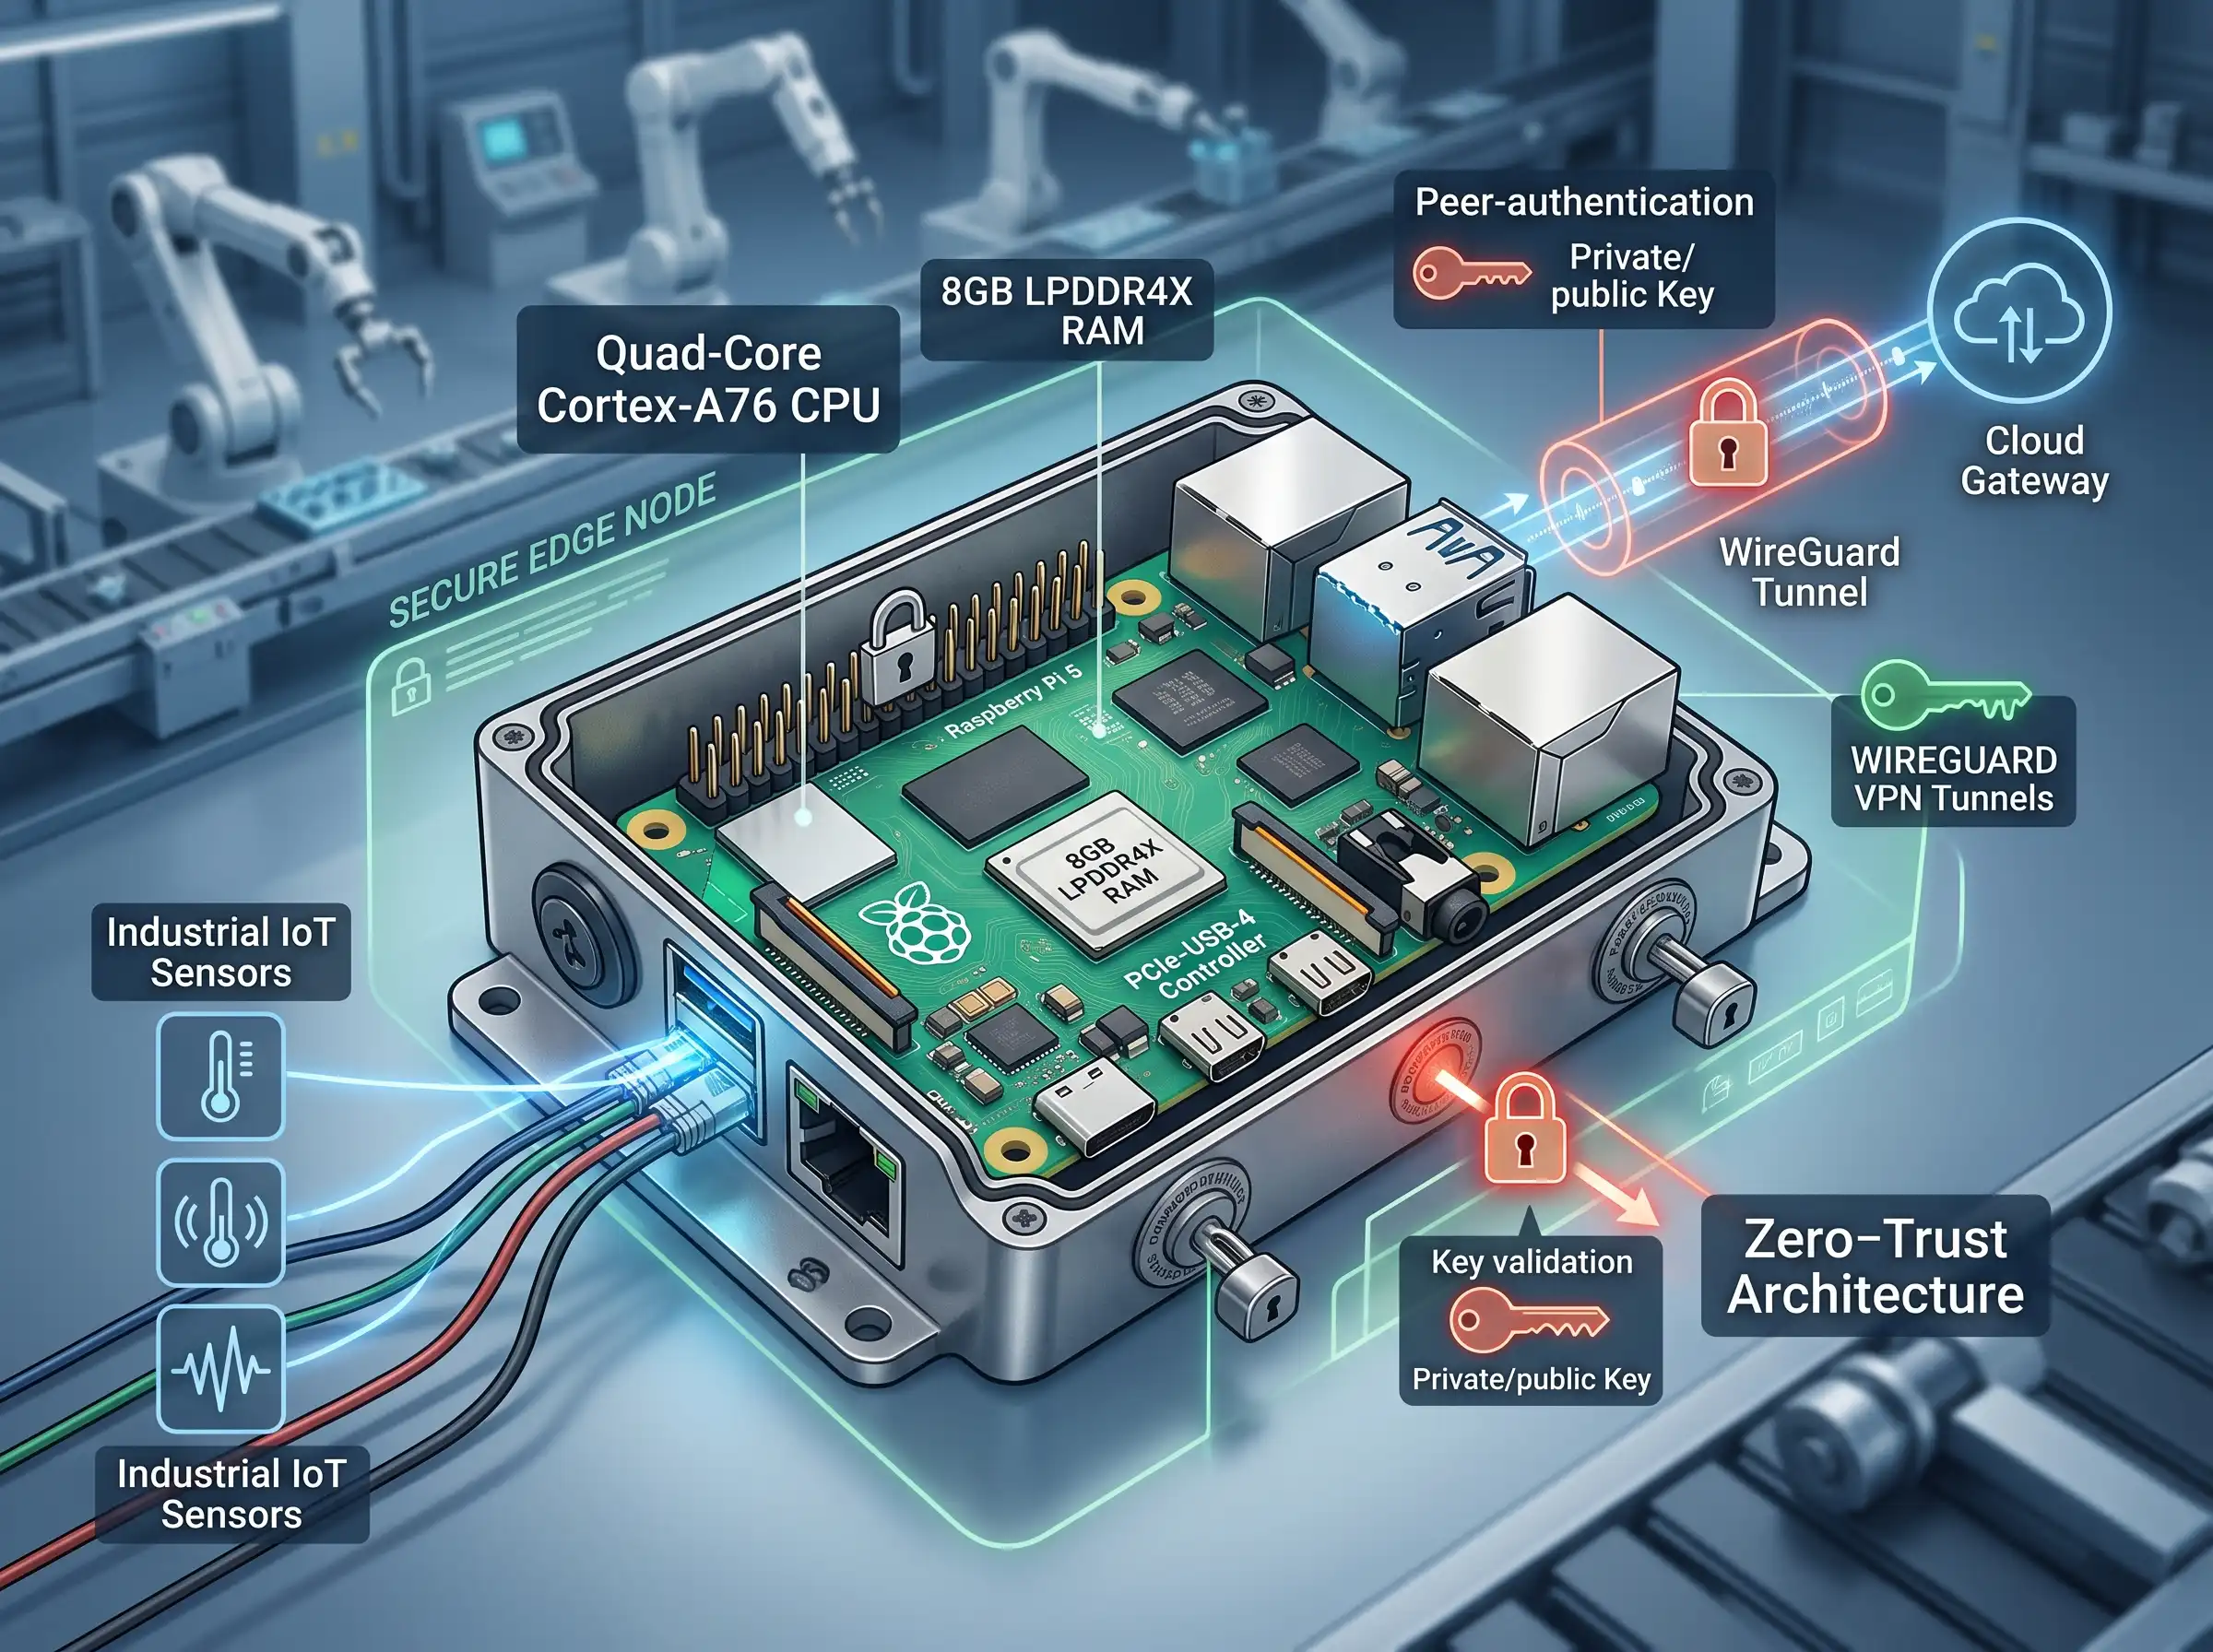
Why Edge Security Matters Now
The past few years have seen a massive surge in remote sensor deployments across factories, energy grids, and logistics hubs. At the same time, the European Union’s data‑localization rules require that sensitive data stay within national borders unless it travels through a trusted, auditable channel. When thousands of cheap compute units sit on factory floors, each becomes a potential entry point for ransomware, espionage, or sabotage. A robust security posture at the edge therefore protects not only the data itself but also the broader corporate network and the physical processes that depend on it.
Remote sensor surge and EU data‑localization
Industrial IoT (IIoT) devices generate telemetry that must be processed close to the source to meet latency requirements. Edge nodes aggregate this data before forwarding it to a central cloud or on‑premises data lake. EU regulations such as the GDPR and the forthcoming Data Governance Act make it mandatory to keep personal or critical operational data on‑premises unless a secure, documented tunnel is used. This creates a clear need for edge nodes that are both lightweight and cryptographically trustworthy.
Threat landscape at the edge
- Physical tampering – devices are often installed in unsecured locations.
- Network sniffing – unsecured Wi‑Fi or Ethernet can expose clear‑text traffic.
- Malware injection – default passwords and unused services are common attack vectors.
- Supply‑chain compromise – unverified firmware can embed backdoors.
Addressing these risks starts with a solid hardware foundation and a disciplined software hardening process.
Choosing the Right Hardware: Raspberry Pi 5 Overview
The Raspberry Pi 5 offers a compelling mix of performance, cost, and community support that makes it ideal for edge‑computing workloads. Its quad‑core Arm Cortex‑A76 CPU, up to 8 GB of LPDDR4X RAM, and gigabit Ethernet provide enough headroom for sensor aggregation, lightweight AI inference, and secure networking.
Key specs relevant to security
- Secure Boot support – optional ROM‑based verification of the bootloader.
- Hardware RNG – generates high‑entropy keys for VPNs and encryption.
- PCIe‑compatible USB‑4 controller – enables fast external storage for encrypted logs.
- GPIO pins with optional physical lock – can be disabled via software to prevent tampering.
Peripheral considerations
Beyond the board itself, a rugged enclosure, reliable power supply, and a managed switch are essential. Choose an enclosure with a tamper‑evident seal and consider a UPS module to avoid abrupt power loss, which can corrupt encrypted filesystems.
Preparing a Hardened, Lightweight OS
For industrial edge nodes, a minimal operating system reduces the attack surface and conserves resources. Two popular choices are Raspberry Pi OS Lite (Debian‑based) and Alpine Linux (musl‑based). Both can be stripped down to a core set of utilities while still supporting WireGuard.
Selecting a base OS
Raspberry Pi OS Lite offers out‑of‑the‑box driver support and a familiar apt package manager. Alpine’s apk system yields a smaller footprint, which is valuable when flash storage is limited. The decision often hinges on existing team expertise; the hardening steps are similar for both.
Disk encryption and secure boot
- Flash the OS image onto a high‑quality micro‑SD card or eMMC module.
- During first boot, enable
dm-cryptLUKS encryption for the root partition:sudo cryptsetup luksFormat /dev/mmcblk0p2 sudo cryptsetup open /dev/mmcblk0p2 cryptroot - Update
/etc/fstaband/etc/crypttabto mount the encrypted volume automatically. - If the Pi 5 firmware supports it, enable the optional secure‑boot flag in the Raspberry Pi Imager’s advanced settings.
Encrypted storage ensures that a stolen SD card cannot be read without the passphrase or hardware‑bound key.
Reducing the attack surface
- Disable unnecessary services:
sudo systemctl disable avahi-daemon bluetooth. - Install and configure
ufwto allow only SSH (if needed) and WireGuard UDP port 51820.sudo ufw allow 51820/udp sudo ufw enable - Remove default user
piand create a dedicated, key‑based user.sudo adduser iotadmin --disabled-password sudo usermod -aG sudo iotadmin sudo passwd -l pi - Set
PasswordAuthentication noin/etc/ssh/sshd_configand enforcePermitRootLogin no.
These steps shrink the number of open ports and eliminate weak authentication vectors.
Installing and Configuring WireGuard for Zero‑Trust Networking
WireGuard is a modern VPN protocol that operates at the kernel level, delivering high performance with a tiny code base—ideal for constrained edge devices. Its design aligns perfectly with zero‑trust principles: every peer must present a valid cryptographic key, and traffic is allowed only to explicitly authorized IP ranges.
Installing WireGuard
On Raspberry Pi OS Lite:
sudo apt update
sudo apt install -y wireguard
On Alpine:
sudo apk update
sudo apk add wireguard-toolsGenerating keys and planning topology
Each node needs a permanent private/public key pair. Run the following on the Pi 5 edge node:
wg genkey | tee privatekey | wg pubkey > publickeyStore the private key in /etc/wireguard/privatekey with permissions 600. Collect the public key and share it with the central gateway (or cloud VPN server). The topology typically follows a star pattern: sensors → edge node → gateway.
Creating a persistent configuration
Save the configuration as /etc/wireguard/wg0.conf:
[Interface]
PrivateKey = (contents of privatekey)
Address = 10.0.0.2/24
ListenPort = 51820
[Peer]
PublicKey = (gateway public key)
Endpoint = gateway.example.com:51820
AllowedIPs = 0.0.0.0/0, ::/0
PersistentKeepalive = 25
Enable the service to start on boot:
sudo systemctl enable wg-quick@wg0
sudo systemctl start wg-quick@wg0Enforcing peer authentication and allowed IPs
On the gateway, restrict the edge node to only the sub‑net used by its sensors. For example:
[Peer]
PublicKey = (edge node public key)
AllowedIPs = 10.0.1.0/24
This ensures that even if the edge node is compromised, it cannot route arbitrary traffic through the corporate network—fulfilling the zero‑trust premise.
Automating Hardening and Monitoring
Manual configuration works for a single prototype, but production deployments benefit from automation. Ansible playbooks or lightweight shell scripts can enforce the same hardening steps across dozens of Pi 5 units.
Using Ansible
- hosts: edge_nodes
  become: true
  tasks:
    - name: Install WireGuard
      apt:
        name: wireguard
        state: present
    - name: Deploy wg0.conf
      copy:
        src: files/wg0.conf
        dest: /etc/wireguard/wg0.conf
        mode: '0600'
    - name: Enable and start service
      systemd:
        name: wg-quick@wg0
        enabled: true
        state: started
    - name: Harden SSH
      lineinfile:
        path: /etc/ssh/sshd_config
        regexp: '^#?PasswordAuthentication'
        line: 'PasswordAuthentication no'
    - name: Enable UFW rules
      ufw:
        rule: allow
        port: 51820
proto: udpLog aggregation and health checks
Configure the systemd journal to forward logs to a central syslog server using systemd-journal-remote. Additionally, set up a cron job that pings the gateway every minute; failure triggers an SMS alert via a low‑cost service like Twilio.
*/1 * * * * /usr/bin/curl -s --connect-timeout 5 https://gateway.example.com/heartbeat || /usr/local/bin/alert.shRegular health checks give operators early warning of network partition or key‑mismatch issues.
Deploying in an Industrial IoT Scenario
Imagine a manufacturing line with temperature, vibration, and power sensors. Each sensor streams data over Modbus/TCP to a local Raspberry Pi 5 that aggregates, preprocesses, and forwards encrypted telemetry to a cloud analytics platform.
Example topology
Sensor LAN (10.0.1.0/24) → Raspberry Pi 5 (10.0.0.2) → WireGuard tunnel → Cloud gateway (10.0.0.1)Step‑by‑step deployment checklist
- Flash the hardened OS image onto the SD card.
- Insert the card, power the Pi, and complete the initial key‑based SSH login.
- Run the Ansible playbook to install WireGuard and apply hardening.
- Generate the node’s key pair and register the public key with the central gateway.
- Verify the tunnel with
wg showand confirm thatAllowedIPsrestrict traffic. - Deploy sensor daemons (e.g.,
modbus-tcpcollectors) and point them at the local Pi IP. - Enable log forwarding and health‑check cron jobs.
- Document the physical lock placement and store the encryption passphrase in a vault.
Following this checklist yields a repeatable, auditable edge node that satisfies both performance and compliance requirements.
How can I rotate WireGuard keys without downtime?
Generate a new key pair on the edge node, add the new public key as a secondary peer on the gateway, and update the wg0.conf with the new private key. Once the new tunnel is up, remove the old peer entry. Because WireGuard establishes connections per‑packet, the switch is seamless.
Related posts
View allEdge AI for Drones: TinyML Guide to Deploy Vision Models
Learn how to turn a simple computer‑vision model into a TensorFlow Lite Micro file and flash it onto a low‑power drone board, enabling real‑time edge AI for autonomous flight.
Edge AI for Real‑Time AR Maintenance with Nvidia Jetson Orin NX
Learn how to build a low‑latency edge AI pipeline that overlays real‑time AR maintenance instructions on industrial equipment using Nvidia’s Jetson Orin NX.
Build Ultra‑Fast Edge AI Inference Pipelines on NVIDIA Jetson Orin Nano
Learn how to quantize, optimize, and deploy AI models on the new Jetson Orin Nano for sub‑millisecond edge inference, a must‑read for 5G‑enabled real‑time applications.
Comments (0)
Be the first to share feedback on this post.